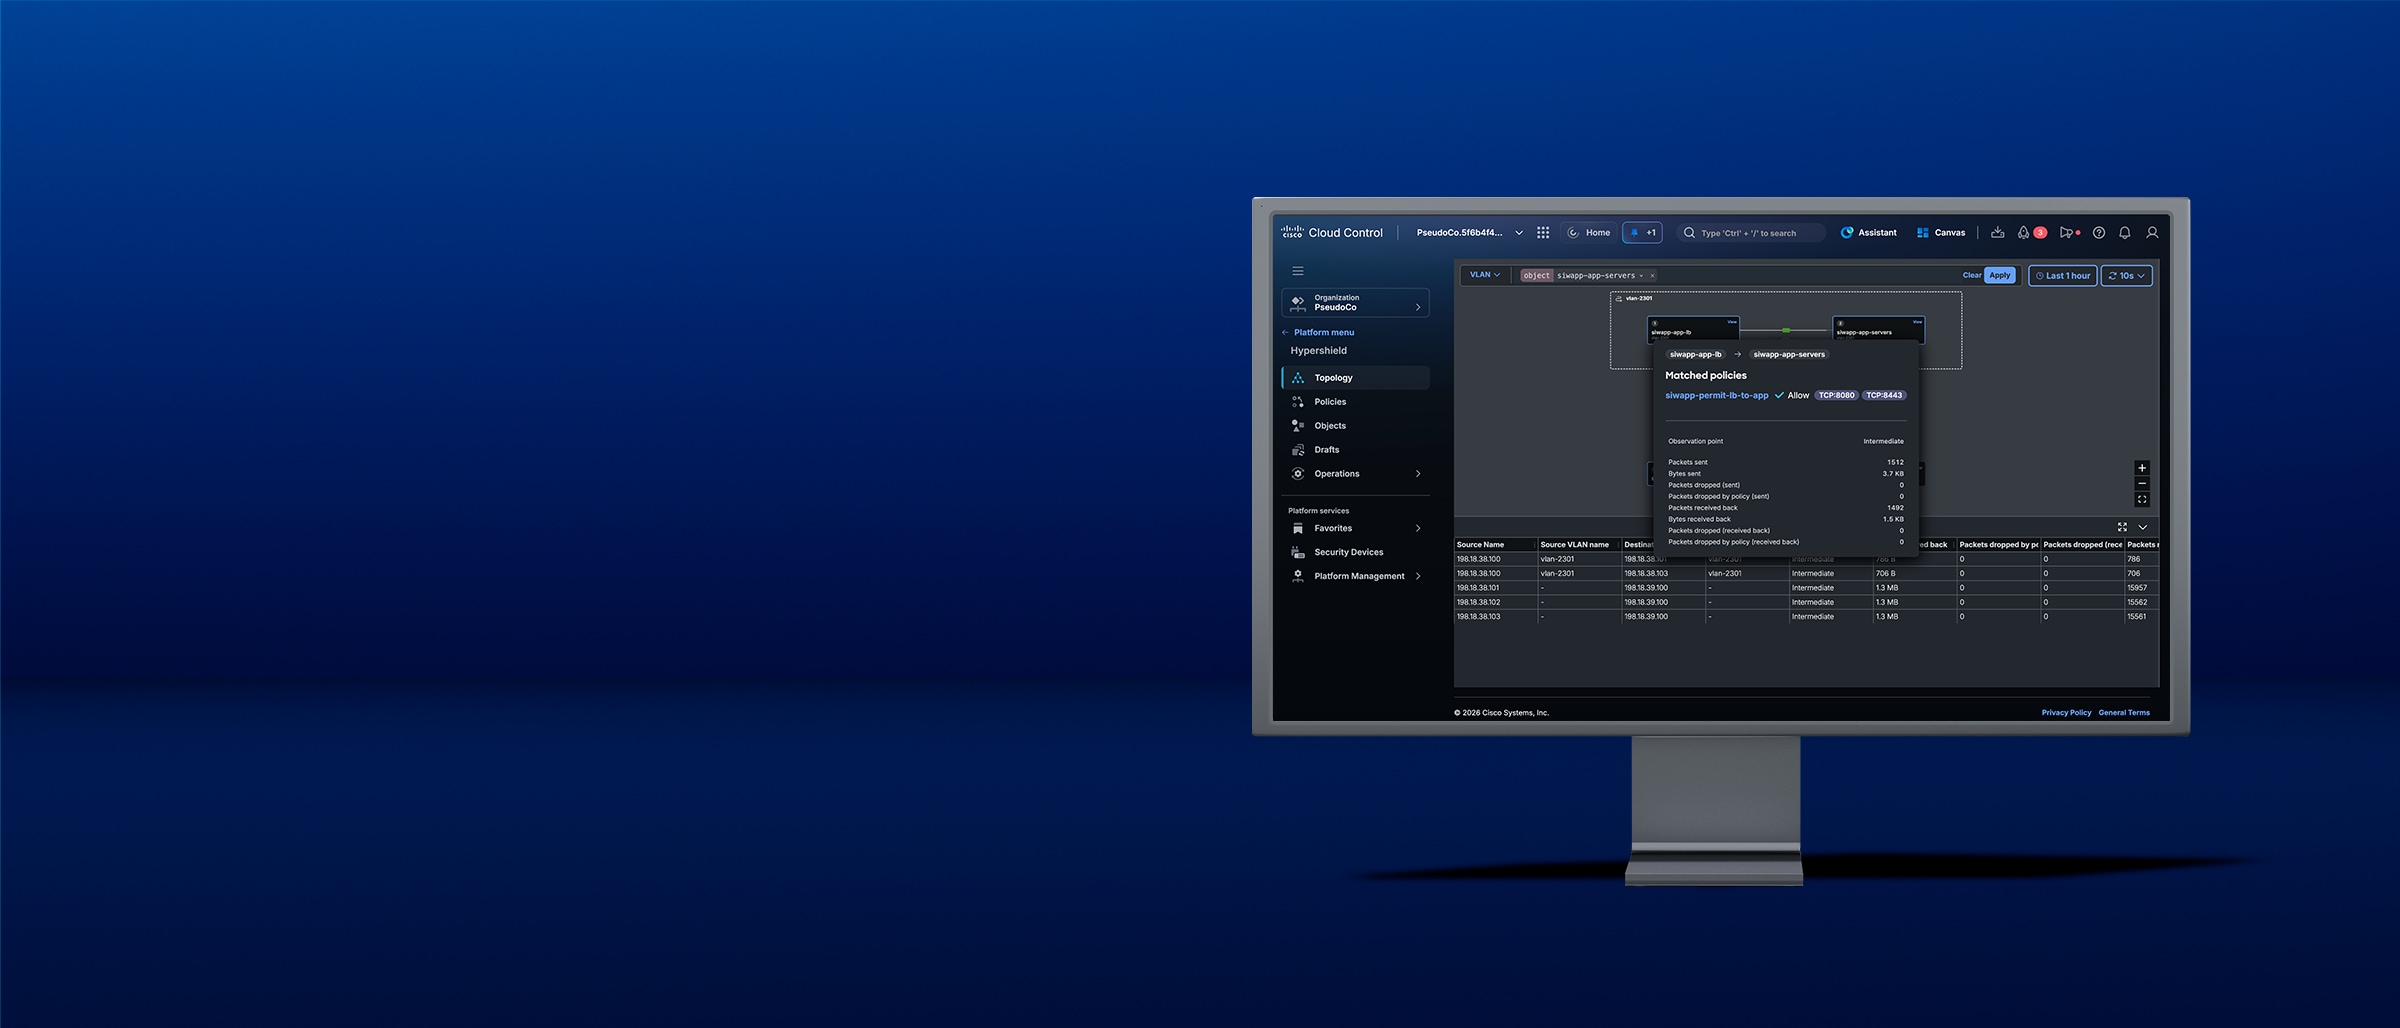
A new approach to segmentation
Fabric-Native Segmentation for Modern Data Centers
Limit lateral movement
Apply hyper-distributed stateful segmentation closer to the source, helping contain threats before they spread across critical applications and workloads.
Turn intent into enforcement
Define policy centrally and place enforcement on the appropriate point in the fabric through Cisco Cloud Control.
Grow security as your fabric grows
Extend protection organically as new racks, workloads, and traffic come online, with enforcement that follows how your data centre evolves.
Designed for modern operations
Security where it matters

Security where traffic flows
Deploy Cisco N9300 Series Smart Switches at the top of rack or as a shared fabric service, aligning protection with your data centre design.

Change policy with confidence
Use observed flow visibility to understand actual policy impact before production.

Reduce security hairpinning
Apply controls closer to where traffic flows and simplify network design.
Where security meets the network
Security infused into the data centre fabric
Cisco N9300 Series Smart Switches embed stateful Layer 3 and Layer 4 enforcement directly into the data centere fabric. By applying segmentation at the top of rack, organisations can secure high-volume east-west traffic at scale while reducing dependence on centralised inspection points.

Policy-controlled enforcement in the fabric
Hypershield gives security teams a consistent way to define stateful L3/L4 segmentation intent while network teams continue to operate the fabric.
Use Cisco Cloud Control to manage policy, visibility, logs, and lifecycle operations across Hypershield enforcement points.
